01 AI Security · Open Source

Break it
before
they do.

An independent AI security research lab. Open-source tooling for LLM red-teaming, adversarial ML, and AI governance.

View on GitHub Explore projects All tools free & open source
10 categories
Full OWASP LLM Top 10 coverage. Every vulnerability class, automated.
100% local
No data leaves your server. Runs on-prem, air-gapped if needed
∞ probes
Coevolutionary engine generates novel attacks that static packs miss

02 What we work on

One lab.
Every layer of the attack surface.

From breaking LLMs to governing them. Six tracks, one method: systematic, evidence-led, reproducible.

01

Offensive

LLM Red-Teaming

Automated and manual adversarial testing of LLM-powered applications. Probe design, evidence collection, and findings mapped to OWASP LLM Top 10 and MITRE ATLAS.

Break My Bot · Garak · PyRIT

02

Research

Adversarial Coevolution

Evolutionary algorithms applied to probe generation. Attack populations adapt against model defences across generations, finding what static probe packs miss.

Active research · 2026–2027

03

Intelligence

OSINT & AI Investigation

Application of AI and open-source intelligence methods to complex investigative contexts. Methodology development, tool evaluation, and practitioner training.

Research & training

04

Governance

AI Governance · ISO 42001

Design and implementation of AI management systems. Risk frameworks, conformity assessments, and governance structures for organisations deploying AI at scale.

ISO/IEC 42001 · Certified

05

Engineering

AI Systems Engineering

Local inference stacks, Dockerised ML pipelines, RAG architectures, and observability tooling. Practical experience from bare metal to production.

Ollama · Docker · Local inference

06

Publishing

AI Security Research

Original research on LLM vulnerabilities, adversarial ML, and alignment failures in production systems. Writing, benchmarks, and open datasets. All free.

Publications · Dec 2027 roadmap


03 Projects
Open Source v0.x · Active dev

Break My Bot

An open-source Dockerised scanner for adversarial testing of LLM-powered applications. Runs automated probes, captures immutable evidence, classifies findings against OWASP LLM Top 10, and generates a structured report. Runs locally; no data leaves your server.

Docker OWASP LLM Top 10 Garak PyRIT Local LLM Judge Evidence-led MITRE ATLAS
Live ctf-range.openblackmountain.com

Capture the Flag

A self-hosted CTF arena for hands-on AI and application security training. Challenges cover prompt injection, jailbreaks, and web vulnerabilities. Students can connect using Kali Linux virtual machines provided by the platform. Runs on the Black Mountain lab. Open to anyone.

Prompt Injection LLM Security Web Self-hosted

04 Research & writing

Technical writing and research notes on LLM security, adversarial ML, AI governance, and AI-assisted investigation. Practitioner-focused, grounded in real tool runs and real threat models.
Follow on GitHub
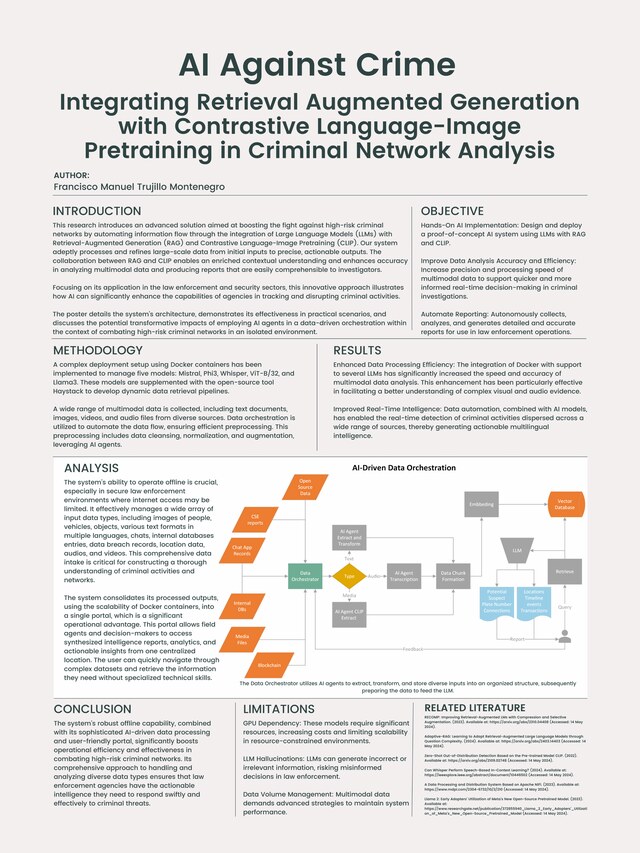
AI Against Crime research poster Published · Poster AI Against Crime: Retrieval-Augmented Generation with Contrastive Language–Image Pretraining in Criminal Network Analysis A proof-of-concept AI system combining RAG and CLIP to enrich multimodal, offline criminal-network analysis, generating actionable intelligence reports for investigators. Research Week 2025 · Ostia, Rome · F. M. Trujillo Montenegro Open poster (PDF) →
Adversarial Coevolution in LLM Red-Teaming
Why static probe packs have a coverage ceiling, and how evolutionary pressure generates attacks that static libraries never contain.
In progress · Q1 2027
Practical OWASP LLM Top 10: Real Findings from Break My Bot
A ground-level walkthrough of each category with real evidence from automated runs against test environments.
Planned · Q4 2026
ISO/IEC 42001 in Practice: AI Governance Without the Jargon
Implementing an AI Management System from the perspective of a practitioner: what matters, what doesn't, and where organisations fail.
Planned · Q4 2026
AI-Assisted OSINT: Tools, Threat Models, and Operational Limits
How AI changes open-source intelligence workflows: capabilities, failure modes, and the limits practitioners need to understand.
Planned · Q1 2027

05 Behind the lab

Founder

Francisco Manuel
Trujillo Montenegro

AI security researcher & systems engineer. Based in Europe.

✓ ISO/IEC 42001 Lead Implementer ✓ LLM Red-Teaming · OWASP LLM Top 10 ✓ OSINT & AI-Assisted Investigation ✓ AI Governance & Risk Frameworks

Open Black Mountain is an independent research lab focused on the security boundaries of AI systems: what breaks, how it breaks, and how to test it rigorously before it reaches production.

The lab produces open-source tooling, research notes, and practitioner-level writing. Everything is built to be reproducible, evidence-led, and free to use.

If you're a researcher, practitioner, or organisation working on AI security and want to collaborate, reach out.

GitHub LinkedIn info@openblackmountain.com